Wamoone Bot API security vulnerabilities
Posted by on
As is often the case with small hobby projects, security can sometimes take a backseat. I discovered an API vulnerability in Wamoone (not to be confused with Wamellow), a new Discord leveling bot, that was conceptually similar to an exploit that affected the DisPing bot in early 2024 .
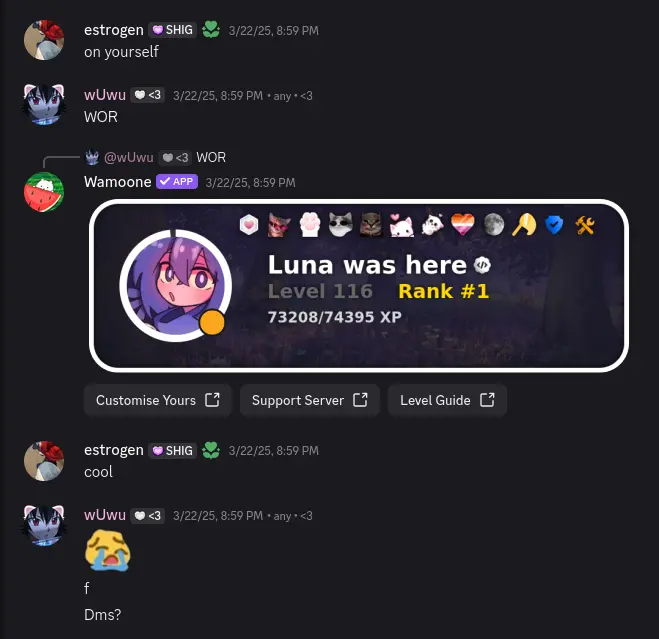
While API requests to the '/v2/custom/rank' endpoint required a valid 'Authorization' bearer token, the API also expected a 'userId' key to be sent within the JSON request body. The critical flaw was a failure in authorization: the server authenticated the request via the bearer token but never verified that the 'userId' in the request body matched the user associated with that token. This allowed any authenticated user to modify the data of any other user simply by changing the 'userId' value in their request.
This vulnerability is a classic example of a broken authorization check. It's crucial to understand the difference:
- Authentication is the process of verifying who you are. When the API checked for a valid bearer token, it was authenticating the request. It successfully confirmed that the request was coming from a valid, logged-in user.
- Authorization is the process of verifying what you are allowed to do. This is where the API failed. It never checked if the authenticated user was authorized to modify the data for the 'userId" specified in the request body.
An authenticated user should — obviously — only be authorized to change their own settings.
A malicious user could send a spoofed POST request like the one below. Even with their own valid bearer token ('abc'), they could change the rank card for a different user ('565852514033860629') to display "Luna was here."
curl 'https://api.wamoone.com/v2/custom/rank' \
  -X POST \
  -H 'Content-Type: application/json' \
  -H 'authorization: Bearer abc' \
  --data-raw '{"customname":"Luna was here","namecolor":"rgb(202,108,146)","userId":"565852514033860629"}'
As I was quick with finding this vulnability, I was able to reported it directly to the developer without it getting abused by bad actors.
Opinion
This incident highlights a critical lesson: developers must diligently test their API routes and ensure all user-supplied data is validated against the authenticated user's permissions. Don't ever trust user input, even from an authenticated source.Regularly testing APIs and engaging with independent security researchers can help prevent such issues. The goal of blog post is not to spread hate or fear but to educate developers, especially those new to the field, on how to write secure applications and avoid common authentication and authorization mistakes.
Author of the Article
